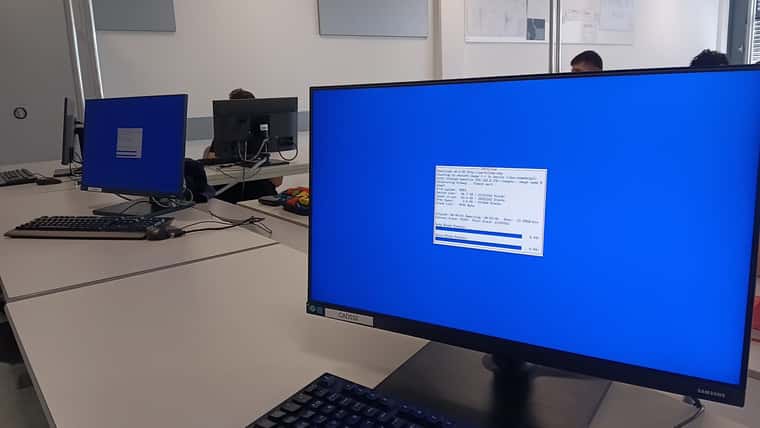
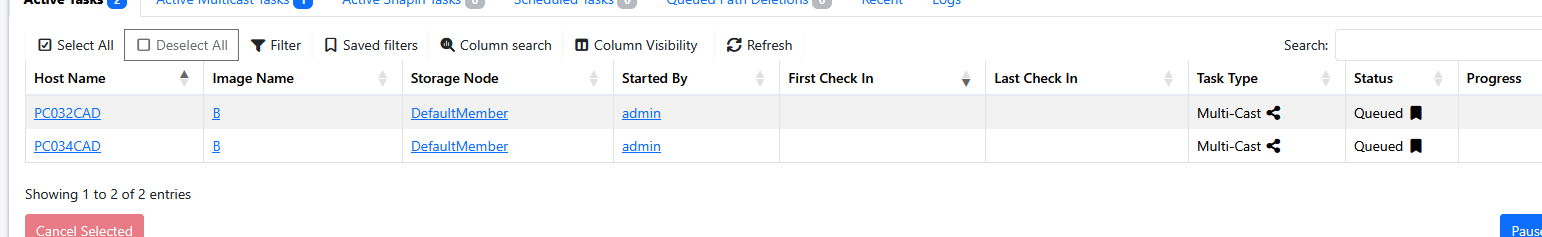
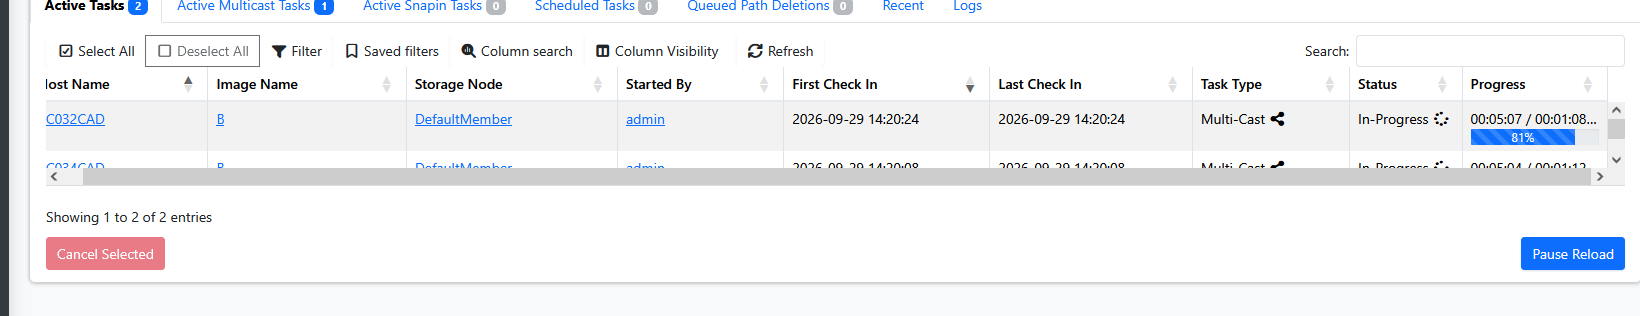
Task 0
-
@kratkale The PXE failure has one cause, and a re-run of the installer fixes it.
On 2026-09-09 you ran the installer with --public-web-cert. The installer saved that setting. It is wrong for your server: your web certificate comes from FOG’s own CA, not from a public CA. Until yesterday, every upgrade stopped before the boot files. Yesterday the upgrade finished, and it applied the saved setting: iPXE now loads boot.php over HTTPS. iPXE cannot verify FOG’s own CA, so it stops with “Permission denied”.
The sudoers errors have a second cause: the sudo package is not installed on your server. Those errors do not stop PXE boot.
Update to 1.6.0-beta.5398 or newer. Then run this on the FOG server, from your fogproject/bin directory:
./installfog.sh -y --no-public-web-cert5398 installs sudo itself.
Then check the boot file:
grep chain /tftpboot/default.ipxeThe line must start with
chain http://192.168.0.196/. If it showshttps://, post the output. Boot one PC before you switch the others back to PXE.The “Detected a web certificate managed outside FOG” message was wrong. 5398 fixes it. It does not affect PXE boot.
5398 also warns if --public-web-cert is set on a certificate from FOG’s own CA.
-
This run will mint a new FOG PKI CA. A CA's name constraints are fixed at the moment it's issued -- widening them later means re-issuing it (rm -rf the CA directory, then re-run). Extra hostnames for this server, space-separated (3 min, blank = none): > Internal domain, e.g. example.local (3 min, blank = none): > * Creating FOG Secure Boot CA.................................Failed * Cannot issue 'FOG Secure Boot CA': the Root CA private key is not on this server (only /opt/fog/snapins/ssl/CA/.fogCA.pem is present). * That is the correct state for an offline root, but issuing a new intermediate needs it. Restore it to: /etc/fog/pki/root/ca/.fogCA.key re-run the installer, then move it back to your vault. Failed! !!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!! !! The installer was not able to run all the way to the end as !! !! something has caused it to fail. The following few lines are !! !! from the error log file which might help us figure out what's !! !! wrong. Please add this information when reporting an error. !! !! As well you might want to take a look at the full error log !! !! in /srv/daten/setup/20260602_wechsel_auf_fog_dev/fogproject/bin/error_logs/fog_error_1.6.0-beta.5401.log !! !!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!!! "EXP_20260918-165800" Attribut "fogsum" von /var/www/fog//service/ipxe/arm_init.cpio.gz auf einen 64-Byte-Wert gesetzt: e7ea9e7d10cc8e0adcf0b000f30db26ef9fb332e100766a5d65b904a03e38f27 '/srv/daten/setup/20260602_wechsel_auf_fog_dev/fogproject/tmp/FOGService.msi' -> '/var/www/fog//client/FOGService.msi' '/srv/daten/setup/20260602_wechsel_auf_fog_dev/fogproject/tmp/SmartInstaller.exe' -> '/var/www/fog//client/SmartInstaller.exe' * This install did not finish, and the checkout has moved since the | last one that did. To put the code back where it was and re-run: | | git -C /srv/daten/setup/20260602_wechsel_auf_fog_dev/fogproject checkout --detach 47067fc7d8a083049cccde47f84af691e7b38ee9 | cd /srv/daten/setup/20260602_wechsel_auf_fog_dev/fogproject/bin && ./installfog.sh | | bin/revertupdate.sh does the same checkout for you, and it can be run | later -- this message appears only now, the script reads the same record. | | Nothing has been reverted for you. Your customizations were already | restored by this run -- see docs/SUPPORTED_CUSTOMIZATIONS.md -- and | bin/restorekernel.sh --list will show the kernel sets kept for you. root@fog:~# -
@kratkale Two separate things. The first gets your PCs booting today.
PXE boot, now. The installer stopped before it rewrote the boot file, so the file still says https. Change it by hand:
sed -i 's#^chain https://#chain http://#' /tftpboot/default.ipxe
grep chain /tftpboot/default.ipxe
The line must now start with
chain http://192.168.0.196/. Boot one PC to test it. The next complete installer run writes this file again, with http.The installer failure. Your certificates were not changed. The installer stopped before it created anything. The Secure Boot signing files that your settings name are not on disk, so it tried to create new ones. That needs the private key of your FOG root CA, and the key is not at /etc/fog/pki/root/ca/.fogCA.key. Your root certificate is still there, so your FOG clients are not affected.
Please do not delete anything, and do not run the installer with --recreate-CA. That replaces the CA that all your FOG clients trust.
Please post the output of these commands. They show only file names and paths, no key contents:
ls -la /etc/fog/pki /etc/fog/pki/root/ca /etc/fog/pki/secureboot /etc/fog/pki/secureboot/ca /etc/fog/pki/secureboot/leaf /opt/fog/snapins/ssl/CA ls -ld /opt/fog/pki grep -E '^PKI_(root|sb)_' /opt/fog/.fogsettings find / -xdev -name '.fogCA.key' 2>/dev/null -
@Tom-Elliott
no http page from apache …
Verbindung fehlgeschlagen: Firefox kann keine Verbindung zu dem Server unter 192.168.0.196 aufbauen.
reboot did not changeapt-get update , apt-get upgradedid not help
root@fog:~# service apache2 status
× apache2.service - The Apache HTTP Server
     Loaded: loaded (/usr/lib/systemd/system/apache2.service; enabled; preset: enabled)
     Active: failed (Result: exit-code) since Tue 2026-09-29 12:20:58 CEST; 10min ago
 Invocation: 5b8a59017fd34c2ea00f68422b02f286
       Docs: https://httpd.apache.org/docs/2.4/
   Mem peak: 10M
        CPU: 77ms

Sep 29 12:20:58 fog systemd[1]: Starting apache2.service - The Apache HTTP Server...
Sep 29 12:20:58 fog apachectl[892]: AH00526: Syntax error on line 55 of /etc/apache2/sites-enabled/001-fog.conf:
Sep 29 12:20:58 fog apachectl[892]: SSLCertificateFile: file '/opt/fog/pki/web/leaf/.webLeaf.pem' does not exist or is empty
Sep 29 12:20:58 fog systemd[1]: apache2.service: Control process exited, code=exited, status=1/FAILURE
Sep 29 12:20:58 fog systemd[1]: apache2.service: Failed with result 'exit-code'.
Sep 29 12:20:58 fog systemd[1]: Failed to start apache2.service - The Apache HTTP Server.
root@fog:~#
Syntax error on line 55:
root@fog:~# head -n 55 /etc/apache2/sites-enabled/001-fog.conf | tail -n 1 SSLCertificateFile /opt/fog/pki/web/leaf/.webLeaf.pem root@fog:~# -
@kratkale Apache stops because its certificate file is gone. The Secure Boot error last week has the same cause: files under FOG’s PKI directory are missing.
I cannot find the cause without seeing what is left on disk. I asked for this on 2026-09-25, and every new error since then comes from the same missing files. So please run this one command first, before you change anything. It only lists file names and changes nothing:
{ ls -la /opt/fog /etc/fog /etc/fog/pki /etc/fog/pki/root/ca /etc/fog/pki/web /etc/fog/pki/web/leaf /opt/fog/snapins/ssl/CA; ls -ld /opt/fog/pki; find / -xdev \( -name '.fogCA.key' -o -name '.webLeaf.pem' -o -name '.fogWebCA.pem' \) -ls; } > /root/fog-pki-state.txt 2>&1Post the contents of /root/fog-pki-state.txt here.
After that, this brings Apache back with a temporary certificate. Browsers will show a certificate warning, and PXE works again over http:
apt-get install -y ssl-cert
sed -i.orig --follow-symlinks -E \
  -e 's#^([[:space:]]*SSLCertificateFile)[[:space:]].*#\1 /etc/ssl/certs/ssl-cert-snakeoil.pem#' \
  -e 's#^([[:space:]]*SSLCertificateKeyFile)[[:space:]].*#\1 /etc/ssl/private/ssl-cert-snakeoil.key#' \
  -e 's#^([[:space:]]*)(SSLCertificateChainFile|SSLCACertificateFile|SSLVerifyClient|SSLVerifyDepth)#\1\# \2#' \
  /etc/apache2/sites-enabled/001-fog.conf
apachectl configtest && systemctl restart apache2
grep chain /tftpboot/default.ipxe
The sed keeps your original file as /etc/apache2/sites-available/001-fog.conf.orig. The last line must start with
chain http://.Do not run the installer again until we know where your CA files are. It would fail the same way.
-
@Tom-Elliott said in Task 0:
root@fog:~# ls -la /etc/fog/pki /etc/fog/pki/root/ca /etc/fog/pki/secureboot /etc/fog/pki/secureboot/ca /etc/fog/pki/secureboot/leaf /opt/fog/snapins/ssl/CA
/etc/fog/pki:
insgesamt 16
drwxr-xr-x 4 root root 4096 25. Sep 16:38 .
drwxr-xr-x 4 root root 4096 25. Sep 16:38 ..
drwxr-xr-x 3 root root 4096 25. Sep 16:38 root
drwxr-xr-x 4 root root 4096 25. Sep 16:38 secureboot

/etc/fog/pki/root/ca:
insgesamt 8
drwx------ 2 root root 4096 25. Sep 16:38 .
drwxr-xr-x 3 root root 4096 25. Sep 16:38 ..
lrwxrwxrwx 1 root root   34 25. Sep 16:38 .fogCA.pem -> /opt/fog/snapins/ssl/CA/.fogCA.pem

/etc/fog/pki/secureboot:
insgesamt 16
drwxr-xr-x 4 root root 4096 25. Sep 16:38 .
drwxr-xr-x 4 root root 4096 25. Sep 16:38 ..
drwx------ 2 root root 4096 25. Sep 16:38 ca
drwxr-xr-x 2 root root 4096 25. Sep 16:38 leaf

/etc/fog/pki/secureboot/ca:
insgesamt 8
drwx------ 2 root root 4096 25. Sep 16:38 .
drwxr-xr-x 4 root root 4096 25. Sep 16:38 ..

/etc/fog/pki/secureboot/leaf:
insgesamt 8
drwxr-xr-x 2 root root 4096 25. Sep 16:38 .
drwxr-xr-x 4 root root 4096 25. Sep 16:38 ..

/opt/fog/snapins/ssl/CA:
insgesamt 16
drwxrwxr-x 2 fogproject www-data 4096  8. Sep 22:17 .
drwxrwxr-x 3 fogproject www-data 4096  8. Sep 22:17 ..
-rwxrwxr-x 1 fogproject www-data 1818  2. Mai 13:31 .fogCA.pem
-rwxrwxr-x 1 fogproject www-data   41  8. Sep 22:17 .fogCA.srl
lrwxrwxrwx 1 root       root       33  8. Sep 22:17 .fogWebCA.key -> /etc/fog/pki/web/ca/.fogWebCA.key
lrwxrwxrwx 1 root       root       33  8. Sep 22:17 .fogWebCA.pem -> /etc/fog/pki/web/ca/.fogWebCA.pem
root@fog:~# ls -ld /opt/fog/pki
lrwxrwxrwx 1 root root 12  8. Sep 22:17 /opt/fog/pki -> /etc/fog/pki
root@fog:~# grep -E '^PKI_(root|sb)_' /opt/fog/.fogsettings
PKI_sb_enabled='yes'
PKI_root_dir='/etc/fog/pki'
PKI_root_ca_cert='/opt/fog/snapins/ssl/CA/.fogCA.pem'
PKI_root_ca_key='/etc/fog/pki/root/ca/.fogCA.key'
PKI_sb_ca_cert=''
PKI_sb_codesign_cert=''
PKI_sb_codesign_key=''
root@fog:~# find / -xdev -name '.fogCA.key' 2>/dev/null
/opt/fog/service/etc/pki/root/ca/.fogCA.key
root@fog:~#
Sorry—I had to work—here are the expenses from earlier
-
@Tom-Elliott said in Task 0:
Post the contents of /root/fog-pki-state.txt here.
root@fog:~# { ls -la /opt/fog /etc/fog /etc/fog/pki /etc/fog/pki/root/ca /etc/fog/pki/web /etc/fog/pki/web/leaf /opt/fog/snapins/ssl/CA; ls -ld /opt/fog/pki; find / -xdev ( -name ‘.fogCA.key’ -o -name ‘.webLeaf.pem’ -o -name ‘.fogWebCA.pem’ ) -ls; } > /root/fog-pki-state.txt 2>&1
root@fog:~# cat /root/fog-pki-state.txt
ls: Zugriff auf ‘/etc/fog/pki/web’ nicht möglich: Datei oder Verzeichnis nicht gefunden
ls: Zugriff auf ‘/etc/fog/pki/web/leaf’ nicht möglich: Datei oder Verzeichnis nicht gefunden
/etc/fog:
insgesamt 20
drwxr-xr-x 4 root root 4096 25. Sep 16:38 .
drwxr-xr-x 100 root root 4096 29. Sep 12:26 …
lrwxrwxrwx 1 root root 31 24. Sep 23:27 config.php -> /opt/fog/service/etc/config.php
drwxr-xr-x 3 root root 4096 25. Sep 16:38 customizations
-rw-r–r-- 1 root root 207 24. Sep 23:27 fog.conf
drwxr-xr-x 4 root root 4096 25. Sep 16:38 pki/etc/fog/pki:
insgesamt 16
drwxr-xr-x 4 root root 4096 25. Sep 16:38 .
drwxr-xr-x 4 root root 4096 25. Sep 16:38 …
drwxr-xr-x 3 root root 4096 25. Sep 16:38 root
drwxr-xr-x 4 root root 4096 25. Sep 16:38 secureboot/etc/fog/pki/root/ca:
insgesamt 8
drwx------ 2 root root 4096 25. Sep 16:38 .
drwxr-xr-x 3 root root 4096 25. Sep 16:38 …
lrwxrwxrwx 1 root root 34 25. Sep 16:38 .fogCA.pem -> /opt/fog/snapins/ssl/CA/.fogCA.pem/opt/fog:
insgesamt 5432
drwxr-xr-x 17 root root 4096 25. Sep 16:38 .
drwxr-xr-x 3 root root 4096 2. Mai 13:31 …
drwxr-xr-x 3 www-data www-data 4096 24. Sep 23:27 agent
drwxr-xr-x 2 root root 4096 24. Sep 23:27 bin
drwxrwxrwt 2 fogproject www-data 4096 29. Sep 12:21 cache
drwxr-xr-x 5 root root 4096 8. Sep 22:17 customizations
-rw------- 1 root root 511 24. Sep 23:27 .fog-pki
-rw------- 1 root root 1026 24. Sep 23:27 .fog-pki-admin
-rw------- 1 root root 511 24. Sep 23:27 .fog-secureboot
-rw-r–r-- 1 root root 2163 24. Sep 23:27 .fog-secureboot-anchor.pem
-rw-r–r-- 1 root root 1704 24. Sep 23:27 .fog-secureboot.pem
-rw------- 1 root root 4407 25. Sep 16:38 .fogsettings
-rw-r–r-- 1 root root 352 25. Sep 16:38 .fogsettings.pub
drwxr-xr-x 7 root root 4096 8. Sep 22:16 lib
drwxr-xr-x 7 root root 4096 25. Sep 09:27 log
drwxr-x— 2 www-data www-data 4096 24. Sep 23:27 nodecert-staging
lrwxrwxrwx 1 root root 12 8. Sep 22:17 pki -> /etc/fog/pki
drwxr-x— 2 www-data www-data 4096 24. Sep 23:27 pkiadmin-staging
drwxr-xr-x 2 root root 4096 24. Sep 23:27 plugins
drwxr-xr-x 2 root root 4096 24. Sep 23:27 reporting
drwxr-x— 2 www-data www-data 4096 8. Sep 21:56 secureboot-staging
drwxr-xr-x 15 root root 4096 24. Sep 23:27 service
drwx------ 2 www-data www-data 5455872 25. Sep 16:06 sessions
drwxrwxr-x 3 fogproject www-data 4096 22. Sep 19:18 snapins
drwxr-xr-x 5 root root 4096 8. Sep 22:16 utils/opt/fog/snapins/ssl/CA:
insgesamt 16
drwxrwxr-x 2 fogproject www-data 4096 8. Sep 22:17 .
drwxrwxr-x 3 fogproject www-data 4096 8. Sep 22:17 …
-rwxrwxr-x 1 fogproject www-data 1818 2. Mai 13:31 .fogCA.pem
-rwxrwxr-x 1 fogproject www-data 41 8. Sep 22:17 .fogCA.srl
lrwxrwxrwx 1 root root 33 8. Sep 22:17 .fogWebCA.key -> /etc/fog/pki/web/ca/.fogWebCA.key
lrwxrwxrwx 1 root root 33 8. Sep 22:17 .fogWebCA.pem -> /etc/fog/pki/web/ca/.fogWebCA.pem
lrwxrwxrwx 1 root root 12 8. Sep 22:17 /opt/fog/pki -> /etc/fog/pki
786737 0 lrwxrwxrwx 1 root root 33 Sep 8 22:17 /opt/fog/snapins/ssl/CA/.fogWebCA.pem -> /etc/fog/pki/web/ca/.fogWebCA.pem
786719 4 -rwxr-xr-x 1 root root 2009 Sep 8 21:56 /opt/fog/service/etc/pki/web/leaf/.webLeaf.pem
786714 4 -rwxr-xr-x 1 root root 2147 Sep 8 21:56 /opt/fog/service/etc/pki/web/ca/.fogWebCA.pem
786691 4 -r-------- 1 root root 3272 Mai 2 13:31 /opt/fog/service/etc/pki/root/ca/.fogCA.key
root@fog:~# -
@kratkale Thank you, that output shows the cause, and your certificates are not lost.
On FOG 1.5, /etc/fog was a link to /opt/fog/service/etc. The 1.6 upgrade moved your PKI files to /etc/fog/pki, so through that link they landed in /opt/fog/service/etc/pki. A later step of the same upgrade replaced the /etc/fog link with an empty directory. Your files are still in /opt/fog/service/etc/pki, but FOG no longer found them. This is an installer bug, and I am fixing it.
Copy them back.
cp -nnever overwrites a file that already exists:cp -an /opt/fog/service/etc/pki/. /etc/fog/pki/ [ -d /opt/fog/service/etc/customizations ] && cp -an /opt/fog/service/etc/customizations /etc/fog/ ls -la /etc/fog/pki/root/ca /etc/fog/pki/web/leafBoth listings must show real files: .fogCA.key in the first, .webLeaf.pem and .webLeaf.key in the second.
If you ran the Apache sed from my last post, put your original file back:
[ -f /etc/apache2/sites-available/001-fog.conf.orig ] && cp /etc/apache2/sites-available/001-fog.conf.orig /etc/apache2/sites-available/001-fog.confThen start Apache and run the installer, from your fogproject/bin directory:
apachectl configtest && systemctl restart apache2
./installfog.sh -y --no-public-web-cert
grep chain /tftpboot/default.ipxe
The last line must start with
chain http://. If any step fails, post the output of that step. Leave /opt/fog/service/etc/pki where it is for now. -
@Tom-Elliott said in Task 0:
The sed keeps your original file as /etc/apache2/sites-available/001-fog.conf.orig.
root@fog:~# apt-get install -y ssl-cert
sed -i.orig --follow-symlinks -E
-e ‘s#^([[:space:]]SSLCertificateFile)[[:space:]].#\1 /etc/ssl/certs/ssl-cert-snakeoil.pem#’
-e ‘s#^([[:space:]]SSLCertificateKeyFile)[[:space:]].#\1 /etc/ssl/private/ssl-cert-snakeoil.key#’
-e ‘s#^([[:space:]]*)(SSLCertificateChainFile|SSLCACertificateFile|SSLVerifyClient|SSLVerifyDepth)#\1# \2#’
/etc/apache2/sites-enabled/001-fog.conf
apachectl configtest && systemctl restart apache2
grep chain /tftpboot/default.ipxe
Paketlisten werden gelesen… Fertig
Abhängigkeitsbaum wird aufgebaut… Fertig
Statusinformationen werden eingelesen… Fertig
ssl-cert ist schon die neueste Version (1.1.3).
ssl-cert wurde als manuell installiert festgelegt.
0 aktualisiert, 0 neu installiert, 0 zu entfernen und 2 nicht aktualisiert.
Syntax OK
chain http://192.168.0.196/fog/service/ipxe/boot.php##params
root@fog:~# service apache2 stauts
Usage: apache2 {start|stop|graceful-stop|restart|reload|force-reload}
root@fog:~# service apache2 status
● apache2.service - The Apache HTTP Server
Loaded: loaded (/usr/lib/systemd/system/apache2.service; enabled; preset: enabled)
Active: active (running) since Tue 2026-09-29 14:03:16 CEST; 30s ago
Invocation: aeea41b42d844b308af3e4c634c0439f
Docs: https://httpd.apache.org/docs/2.4/
Process: 24502 ExecStart=/usr/sbin/apachectl start (code=exited, status=0/SUCCESS)
Main PID: 24505 (apache2)
Tasks: 6 (limit: 4594)
Memory: 19.1M (peak: 19.2M)
CPU: 129ms
CGroup: /system.slice/apache2.service
├─24505 /usr/sbin/apache2 -k start
├─24508 /usr/sbin/apache2 -k start
├─24509 /usr/sbin/apache2 -k start
├─24510 /usr/sbin/apache2 -k start
├─24511 /usr/sbin/apache2 -k start
└─24512 /usr/sbin/apache2 -k startSep 29 14:03:15 fog systemd[1]: Starting apache2.service - The Apache HTTP Server…
Sep 29 14:03:16 fog systemd[1]: Started apache2.service - The Apache HTTP Server.
root@fog:~# -
@Tom-Elliott said in Task 0:
Both listings must show real files: .fogCA.key in the first, .webLeaf.pem and .webLeaf.key in the second.
root@fog:~# cp -an /opt/fog/service/etc/pki/. /etc/fog/pki/ [ -d /opt/fog/service/etc/customizations ] && cp -an /opt/fog/service/etc/customizations /etc/fog/ ls -la /etc/fog/pki/root/ca /etc/fog/pki/web/leaf /etc/fog/pki/root/ca: insgesamt 12 drwx--x--x 2 root root 4096 8. Sep 22:07 . drwxr-xr-x 3 root root 4096 8. Sep 22:17 .. -r-------- 1 root root 3272 2. Mai 13:31 .fogCA.key lrwxrwxrwx 1 root root 34 25. Sep 16:38 .fogCA.pem -> /opt/fog/snapins/ssl/CA/.fogCA.pem /etc/fog/pki/web/leaf: insgesamt 36 drwx--x--x 2 root root 4096 24. Sep 23:27 . drwxr-xr-x 4 root root 4096 8. Sep 21:56 .. -rwxr-xr-x 1 root root 2147 24. Sep 23:27 .webChain.pem -rwxr-xr-x 1 root root 4156 24. Sep 23:27 .webFullChain.pem -rwxr-xr-x 1 root root 1769 8. Sep 21:56 .webLeaf.csr -rwx--x--x 1 root root 3272 8. Sep 21:56 .webLeaf.key -rwxr-xr-x 1 root root 2009 8. Sep 21:56 .webLeaf.pem -rwxr-xr-x 1 root root 45 8. Sep 21:56 .webLeaf.sans root@fog:~# -
@Tom-Elliott said in Task 0:
[ -f /etc/apache2/sites-available/001-fog.conf.orig ] && cp /etc/apache2/sites-available/001-fog.conf.orig /etc/apache2/sites-available/001-fog.conf
root@fog:~# [ -f /etc/apache2/sites-available/001-fog.conf.orig ] && cp /etc/apache2/sites-available/001-fog.conf.orig /etc/apache2/sites-available/001-fog.conf root@fog:~# -
@Tom-Elliott said in Task 0:
apachectl configtest && systemctl restart apache2
./installfog.sh -y --no-public-web-cert
grep chain /tftpboot/default.ipxeroot@fog:~# apachectl configtest && systemctl restart apache2 ./installfog.sh -y --no-public-web-cert grep chain /tftpboot/default.ipxe Syntax OK -bash: ./installfog.sh: Datei oder Verzeichnis nicht gefunden chain http://192.168.0.196/fog/service/ipxe/boot.php##params root@fog:~#I’ll now run the installfog in the correct dir
-
@Tom-Elliott said in Task 0:
./installfog.sh -y --no-public-web-cert
root@fog:~/FOG_SERVER_Updates_durchführen# ./301_updaten_working-1.6 IPFire muss FOG durchlassen! Bereits auf 'working-1.6' Ihr Branch ist auf demselben Stand wie 'origin/working-1.6'. remote: Enumerating objects: 136, done. remote: Counting objects: 100% (65/65), done. remote: Compressing objects: 100% (38/38), done. remote: Total 136 (delta 36), reused 45 (delta 27), pack-reused 71 (from 1) Empfange Objekte: 100% (136/136), 797.82 KiB | 8.49 MiB/s, fertig. Löse Unterschiede auf: 100% (69/69), abgeschlossen mit 11 lokalen Objekten. Von https://github.com/fogproject/fogproject 7bcae674c..ff62c1f17 working-1.6 -> origin/working-1.6 efc921957..e98fdd6cb dev-branch -> origin/dev-branch * [neuer Branch] fix/etc-fog-symlink-orphans-pki -> origin/fix/etc-fog-symlink-orphans-pki * [neuer Branch] rc-1.6.0 -> origin/rc-1.6.0 * [neues Tag] 1.6.0-RC-1 -> 1.6.0-RC-1 Aktualisiere 7bcae674c..ff62c1f17 Fast-forward .githooks/lib/fog-version.sh | 36 +++++++++++++++++++++++++++++------- bin/bootstrap.sh | 24 +++++++++++++++++++++--- bin/updatefog.sh | 12 ++++++++++++ lib/common/functions.sh | 111 ++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++----------- packages/web/src/Base/FOGPage.php | 19 ++++++++++++------- tests/bootstrap-installer.test.sh | 5 +++++ tests/external-cert-detection.test.sh | 37 +++++++++++++++++++++++++++++++++++++ tests/fog-version-release-tag.test.sh | 36 +++++++++++++++++++++++++++++++++++- tests/rc-channel-resolution.test.sh | 18 ++++++++++++++++++ tests/svc-bashrc-silent-for-sftp.test.sh | 68 ++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++++ 10 files changed, 337 insertions(+), 29 deletions(-) create mode 100644 tests/svc-bashrc-silent-for-sftp.test.sh Weiter mit beliebiger Taste ^C root@fog:~/FOG_SERVER_Updates_durchführen# ./303_fog_installieren Installing LSB_Release as needed * Attempting to get release information.......................Done ================================== === ==== ===== ==== === ========= == === == === === ======== ==== == ==== === === ======== ==== == ========= === ==== ==== == ========= === ======== ==== == === === === ======== ==== == ==== === === ========= == === == === === ========== ===== ==== ================================== ===== Free Opensource Ghost ====== ================================== ============ Credits ============= = https://fogproject.org/Credits = ================================== == Released under GPL Version 3 == ================================== Version: 1.6.0-beta.5417 Installer/Updater * Found FOG Settings from previous install at: /opt/fog/.fogsettings * Performing upgrade using these settings Starting Debian based Installation ###################################################################### # FOG now has everything it needs for this setup, but please # # understand that this script will overwrite any setting you may # # have setup for services like DHCP, apache, pxe, tftp, and NFS. # ###################################################################### # It is not recommended that you install this on a production system # # as this script modifies many of your system settings. # ###################################################################### # This script should be run by the root user. # # It will prepend the running with sudo if root is not set # ###################################################################### # Please see our wiki for more information at: # ###################################################################### # https://wiki.fogproject.org/wiki/index.php # ###################################################################### * Here are the settings FOG will use: * Base Linux: Debian * Detected Linux Distribution: Debian GNU/Linux * Interface: eno1 * Server IP Address: 192.168.0.196 * Server Subnet Mask: 255.255.0.0 * Hostname: fog.mm.htlwien10.at * Installation Type: Normal Server * Internationalization: No * Image Storage Location: /images * Using FOG DHCP: No * DHCP will NOT be setup but you must setup your | current DHCP server to use FOG for PXE services. * On a Linux DHCP server you must set: next-server and filename * On a Windows DHCP server you must set options 066 and 067 * Option 066/next-server is the IP of the FOG Server: (e.g. 192.168.0.196) * Option 067/filename is the bootfile, per client architecture: | BIOS / legacy undionly.kkpxe | 32-bit UEFI i386-efi/snponly.efi | 64-bit UEFI secureboot/snponly-shimx64.efi | ARM64 UEFI secureboot/arm64-efi/snponly-shimaa64.efi * The secureboot/ files are the signed chain. They boot the same | whether Secure Boot is enabled or not, so they are the right | answer for every 64-bit UEFI client, not just the ones enforcing | it. There is no signed 32-bit chain -- those clients must have | Secure Boot disabled to netboot at all. | See https://docs.fogproject.org/en/latest/secure-boot-netboot * Send OS Name, OS Version, and FOG Version: Yes * Web protocol: https * Netboot (PXE) protocol: https * Force HTTP->HTTPS redirect: No * Web certificate chains to a public root: No * Rebuild iPXE with your CA: No * Installation Started * Testing internet connection.................................Done * Adjusting repository (can take a long time for cleanup).....OK * Preparing Package Manager...................................OK * Reading package state.......................................OK * Packages to be installed: apache2 attr bc build-essential cpp curl efitools g++ gawk gcc gcc-aarch64-linux-gnu genisoimage git gzip htmldoc isolinux jq lftp libapache2-mod-php libc6 libcurl4t64 liblzma-dev m4 mariadb-client mariadb-server net-tools nfs-kernel-server openssh-server php php-bcmath php-cli php-curl php-fpm php-gd php-json php-ldap php-mbstring php-mysql php-ssh2 sbsigntool sudo tar tftpd-hpa tftp-hpa unzip vsftpd wget zlib1g * Skipping package: apache2.................................(Already Installed) * Skipping package: attr....................................(Already Installed) * Skipping package: bc......................................(Already Installed) * Skipping package: build-essential.........................(Already Installed) * Skipping package: cpp.....................................(Already Installed) * Skipping package: curl....................................(Already Installed) * Skipping package: efitools................................(Already Installed) * Skipping package: g++.....................................(Already Installed) * Skipping package: gawk....................................(Already Installed) * Skipping package: gcc.....................................(Already Installed) * Skipping package: gcc-aarch64-linux-gnu...................(Already Installed) * Skipping package: genisoimage.............................(Already Installed) * Skipping package: git.....................................(Already Installed) * Skipping package: gzip....................................(Already Installed) * Skipping package: htmldoc.................................(Already Installed) * Skipping package: isolinux................................(Already Installed) * Skipping package: jq......................................(Already Installed) * Skipping package: lftp....................................(Already Installed) * Skipping package: libapache2-mod-php......................(Already Installed) * Skipping package: libc6...................................(Already Installed) * Skipping package: libcurl4t64.............................(Already Installed) * Skipping package: liblzma-dev.............................(Already Installed) * Skipping package: m4......................................(Already Installed) * Skipping package: mariadb-client..........................(Already Installed) * Skipping package: mariadb-server..........................(Already Installed) * Skipping package: net-tools...............................(Already Installed) * Skipping package: nfs-kernel-server.......................(Already Installed) * Skipping package: openssh-server..........................(Already Installed) * Skipping package: php.....................................(Already Installed) * Skipping package: php-bcmath..............................(Already Installed) * Skipping package: php-cli.................................(Already Installed) * Skipping package: php-curl................................(Already Installed) * Skipping package: php-fpm.................................(Already Installed) * Skipping package: php-gd..................................(Already Installed) * Skipping package: php-json................................(Already Installed) * Skipping package: php-ldap................................(Already Installed) * Skipping package: php-mbstring............................(Already Installed) * Skipping package: php-mysql...............................(Already Installed) * Skipping package: php-ssh2................................(Already Installed) * Skipping package: sbsigntool..............................(Already Installed) * Skipping package: sudo....................................(Already Installed) * Skipping package: tar.....................................(Already Installed) * Skipping package: tftpd-hpa...............................(Already Installed) * Skipping package: tftp-hpa................................(Already Installed) * Skipping package: unzip...................................(Already Installed) * Skipping package: vsftpd..................................(Already Installed) * Skipping package: wget....................................(Already Installed) * Skipping package: zlib1g..................................(Already Installed) * Updating packages as needed.................................OK * Confirming package installation * Checking package: apache2...................................OK * Checking package: attr......................................OK * Checking package: bc........................................OK * Checking package: build-essential...........................OK * Checking package: cpp.......................................OK * Checking package: curl......................................OK * Checking package: efitools..................................OK * Checking package: g++.......................................OK * Checking package: gawk......................................OK * Checking package: gcc.......................................OK * Checking package: gcc-aarch64-linux-gnu.....................OK * Checking package: genisoimage...............................OK * Checking package: git.......................................OK * Checking package: gzip......................................OK * Checking package: htmldoc...................................OK * Checking package: isolinux..................................OK * Checking package: jq........................................OK * Checking package: lftp......................................OK * Checking package: libapache2-mod-php........................OK * Checking package: libc6.....................................OK * Checking package: libcurl4t64...............................OK * Checking package: liblzma-dev...............................OK * Checking package: m4........................................OK * Checking package: mariadb-client............................OK * Checking package: mariadb-server............................OK * Checking package: net-tools.................................OK * Checking package: nfs-kernel-server.........................OK * Checking package: openssh-server............................OK * Checking package: php.......................................OK * Checking package: php-bcmath................................OK * Checking package: php-cli...................................OK * Checking package: php-curl..................................OK * Checking package: php-fpm...................................OK * Checking package: php-gd....................................OK * Checking package: php-json..................................OK * Checking package: php-ldap..................................OK * Checking package: php-mbstring..............................OK * Checking package: php-mysql.................................OK * Checking package: php-ssh2..................................OK * Checking package: sbsigntool................................OK * Checking package: sudo......................................OK * Checking package: tar.......................................OK * Checking package: tftpd-hpa.................................OK * Checking package: tftp-hpa..................................OK * Checking package: unzip.....................................OK * Checking package: vsftpd....................................OK * Checking package: wget......................................OK * Checking package: zlib1g....................................OK * Configuring services * Setting up fogproject user..................................Skipped * Locking fogproject as a system account......................OK * Setting up fogproject password..............................OK * Stopping FOGMulticastManager.service Service................OK * Stopping FOGImageReplicator.service Service.................OK * Stopping FOGSnapinReplicator.service Service................OK * Stopping FOGScheduler.service Service.......................OK * Stopping FOGPingHosts.service Service.......................OK * Stopping FOGSnapinHash.service Service......................OK * Stopping FOGImageSize.service Service.......................OK * Stopping FOGFileDeleter.service Service.....................OK * Stopping FOGPluginRunner.service Service....................OK * Stopping FOGRetentionRunner.service Service.................OK * Stopping FOGAgentReleaseSync.service Service................OK * Setting up and starting MySQL...............................OK * Testing connection to database..............................OK * Setting up MySQL user and database..........................Skipped * Backing up user reports.....................................Done * Backing up customizations...................................OK * Downloading plugins (v1.6.24)...............................OK * Stopping web service........................................OK * Setting up Apache and PHP files.............................OK * Testing and removing symbolic links if found................OK * Backing up old data.........................................OK * Copying new files to web folder.............................OK * Dropping the stale class file lists.........................OK * Creating config file........................................OK * Creating paths file.........................................OK * Creating redirection index file.............................Skipped * Downloading kernel, init and fog-client binaries............Done * Copying binaries to destination paths.......................OK * Signing FOS kernels and Memtest86+ for Secure Boot..........Done * Installing Secure Boot signing helper.......................Done * Publishing Secure Boot enrollment kit.......................Done * Publishing Secure Boot variable updates.....................Done * Enabling apache2 and fpm services on boot...................OK * Publishing client communication certificate.................OK * Creating auth pub key and cert..............................OK * Resetting SSL Permissions...................................OK * Setting up Apache virtual host (normal).....................OK * Testing Apache configuration................................OK * Configuring PHP FPM.........................................Done * Starting and checking status of web services................OK * Changing permissions on apache log files....................OK * Setting up FOG Services.....................................OK * Creating FOG plugin runner log directory....................OK * Creating FOG retention runner log directory.................OK * Creating FOG agent release sync log directory...............OK * Creating FOS report log directory...........................OK * Creating FOG fault log directory............................OK * Setting FOG service master log ownership....................OK * Creating FOG cache directory................................OK * Creating FOG agent directory................................OK * Creating FOG agent versions directory.......................OK * Creating FOG session directory..............................OK * Creating FOG plugin directory...............................OK * Checking web server serves FOG..............................Done * Backing up database.........................................Done * Updating Database...........................................OK * Verifying database schema...................................Done * Update fogstorage database password.........................OK * Granting access to fogstorage database user.................Skipped * Setting up storage..........................................OK * Downloading iPXE Secure Boot binaries (v2.0.0-fog.8)........OK * Setting up and starting DHCP Server.........................Skipped * A sample Kea DHCP config for a dedicated/external DHCP server was | written to: /var/www/fog/kea-dhcp4.conf.fog-sample | Copy it to your DHCP server as /etc/kea/kea-dhcp4.conf and adjust the | subnet/pool/routers/domain-name-servers to match that network. | next-server is already set to this FOG server (192.168.0.196). * Downloading iPXE binaries (v2.0.0-fog.8)....................OK * Removing iPXE paths retired in v2.0.0-fog.8.................Done * autoexec/ is gone: every EFI binary in the TFTP root reads autoexec.ipxe now, so the duplicate tree served no purpose. * 10secdelay/ keeps its BIOS builds and has lost its EFI ones. On EFI the delay is installfog.sh --boot-delay, which writes a sleep into autoexec.ipxe; an EMBED-marked .efi sitting next to a root autoexec.ipxe panics the client it boots. * If any DHCP server hands out a boot filename starting "autoexec/", drop that prefix -- autoexec/snponly.efi becomes snponly.efi. If one names 10secdelay/<something>.efi, point it at the same file without the 10secdelay/ prefix and set --boot-delay instead. * Configuring default iPXE file...............................OK * Setting up and starting TFTP Server.........................OK * Restoring customizations....................................OK * Signing rEFInd for Secure Boot..............................Done * Signing iPXE binaries for Secure Boot.......................Done (15) * Publishing local ESP boot archives..........................Done (3) * Setting up and starting VSFTP Server........................OK * Setting up FOG Snapins......................................OK * Restricting private key access..............................OK ################################################################### # The CA private key for this server is on this server, readable # # only by root: # # /etc/fog/pki/root/ca/.fogCA.key # # # # That protects it from a compromise of the web application, but # # not from a compromise of the machine. To move it to a vault: # # /opt/fog/bin/fog-offline-ca-key /mnt/vault # # # # Day to day nothing needs it. Restore it only to issue a new # # intermediate, or a certificate for a new storage node. # # # # The Secure Boot CA private key is also on this server, # # readable only by root: # # /etc/fog/pki/secureboot/ca/.fogSBCA.key # # # # Restore it to issue a new Secure Boot intermediate, or a # # new signing leaf. To move it to a vault: # # /opt/fog/bin/fog-offline-ca-key /mnt/vault --zone secureboot # ################################################################### * Installing node certificate signing helper..................Done * Installing the certificate management helper................Done * Trusting the FOG CA on this server..........................Done * Setting up UDPCast..........................................OK * Configuring UDPCast.........................................OK * Building UDPCast............................................OK * Installing UDPCast..........................................OK * Installing FOG System Scripts...............................OK * Configuring FOG System Services * Setting permissions on FOGMulticastManager.service script...OK * Enabling FOGMulticastManager.service Service................OK * Setting permissions on FOGImageReplicator.service script....OK * Enabling FOGImageReplicator.service Service.................OK * Setting permissions on FOGSnapinReplicator.service script...OK * Enabling FOGSnapinReplicator.service Service................OK * Setting permissions on FOGScheduler.service script..........OK * Enabling FOGScheduler.service Service.......................OK * Setting permissions on FOGPingHosts.service script..........OK * Enabling FOGPingHosts.service Service.......................OK * Setting permissions on FOGSnapinHash.service script.........OK * Enabling FOGSnapinHash.service Service......................OK * Setting permissions on FOGImageSize.service script..........OK * Enabling FOGImageSize.service Service.......................OK * Setting permissions on FOGFileDeleter.service script........OK * Enabling FOGFileDeleter.service Service.....................OK * Setting permissions on FOGPluginRunner.service script.......OK * Enabling FOGPluginRunner.service Service....................OK * Setting permissions on FOGRetentionRunner.service script....OK * Enabling FOGRetentionRunner.service Service.................OK * Setting permissions on FOGAgentReleaseSync.service script...OK * Enabling FOGAgentReleaseSync.service Service................OK * Starting FOGMulticastManager.service Service................OK * Starting FOGImageReplicator.service Service.................OK * Starting FOGSnapinReplicator.service Service................OK * Starting FOGScheduler.service Service.......................OK * Starting FOGPingHosts.service Service.......................OK * Starting FOGSnapinHash.service Service......................OK * Starting FOGImageSize.service Service.......................OK * Starting FOGFileDeleter.service Service.....................OK * Starting FOGPluginRunner.service Service....................OK * Starting FOGRetentionRunner.service Service.................OK * Starting FOGAgentReleaseSync.service Service................OK * Setting up NFS configuration file...........................OK * Setting up exports file.....................................OK * Setting up and starting RPCBind.............................OK * Setting up and starting NFS Server..........................OK * Linking FOG Service config /etc.............................OK * Recording FOG base path.....................................OK * Installing FOG utilities....................................OK * Ensuring node username and passwords match..................Done * Recording fog_git_path/update channel/extra server names....OK * Setting up FOG External Reporting...........................Done * Netboot (PXE) is using HTTP, not HTTPS. Your web UI and API are HTTPS; only iPXE's own fetches are not. iPXE validates TLS strictly and cannot be told to trust a private CA, so an HTTPS netboot against one simply fails. HTTP here is the same exposure a default install has always had, on a pre-boot network. * Secure Boot binaries ARE staged on this server, in every mode. That used to be skipped on any HTTPS install. To enroll a machine, boot it and choose 'Enroll Secure Boot Key' from the FOG menu. * To move netboot onto HTTPS, tell FOG which is true: --public-web-cert your certificate chains to a public root (needs an FQDN, not an IP) --rebuild-ipxe-with-my-ca rebuild iPXE with your CA embedded (slow, and its MOK must be enrolled before a client can netboot) Or force it outright with --netboot-proto https. * Setup complete You can now login to the FOG Management Portal using the information listed below. The login information is only if this is the first install. This can be done by opening a web browser and going to: https://fog.mm.htlwien10.at/fog/management https://192.168.0.196/fog/management Either works -- the certificate covers the address as well as the name, so neither is a name mismatch. The address needs no DNS; the name it is issued for is fog.mm.htlwien10.at. Default User Information Username: fog Password: password root@fog:~# -
@kratkale That run is clean. Every step finished, the sudoers and certificate errors are gone, and all FOG services started.
The summary near the top says “Netboot (PXE) protocol: https”. That line is wrong: it showed the setting from the previous run. The end of the run is correct: netboot uses HTTP. I am fixing the summary line in the installer.
Please check these, in this order:
grep chain /tftpboot/default.ipxe
systemctl is-active FOGMulticastManagerThe first line must start with chain http://192.168.0.196/. The second must say active. Then PXE boot one PC. If it reaches the FOG menu, switch the other PCs back to PXE and try the multicast task again. If a step fails, post the output of that step only.
-
Yay—multicast is working with 2 PCs—now just the snap-ins…
-
@kratkale Good, thank you for confirming.
If a snap-in does not run, open a new topic for it, and post these three things there:
- the snap-in task status from the web UI (Tasks, Active Tasks)
- whether the PC runs the FOG Client or the FOG Agent
- the client log from that PC: C:\fog.log for the FOG Client
Your certificates are the original ones, restored from the old directory. The clients do not need to trust a new CA.
-
@Tom-Elliott
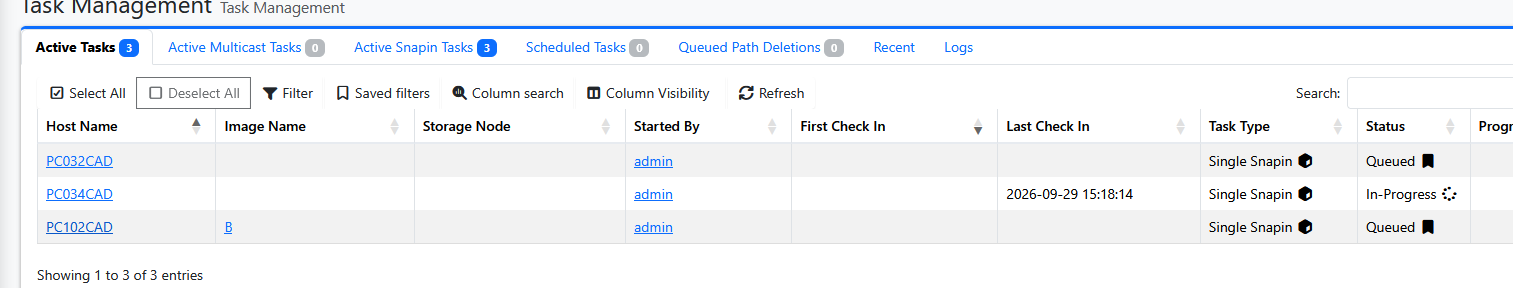
The snap-ins work—the image is displayed on the old computer, but not on the two new ones. -
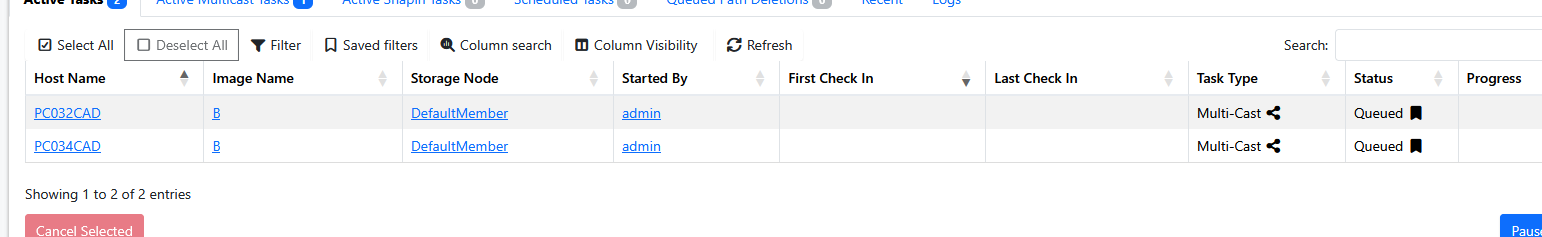
@kratkale I’m not sure what problem you’re trying to solve.
if those 2 machines don’t have a valid image associated, what are you expecting to see for the 'Image Name"? In my head this is expected.