• Recent
    • Unsolved
    • Tags
    • Popular
    • Users
    • Groups
    • Search
    • Register
    • Login
    1. Home
    2. thesmj248
    T
    • Profile
    • Following 0
    • Followers 0
    • Topics 3
    • Posts 5
    • Groups 0

    thesmj248

    @thesmj248

    0
    Reputation
    1
    Profile views
    5
    Posts
    0
    Followers
    0
    Following
    Joined
    Last Online

    thesmj248 Unfollow Follow

    Latest posts made by thesmj248

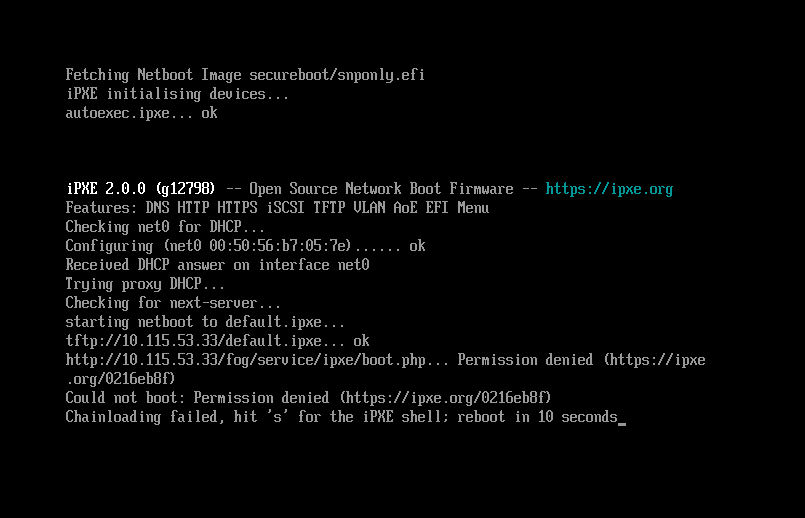
    • IPXE boot no longer works after upgrade to 1.6. Error code 0216eb

      22e054ea-44b0-4fb4-ba06-73e8972954d9-image.png

      Just updated from 1.5.10.(?) (the last stable version) to 1.6.0.14. Was using the FOGUefi mod with 1.5.10 to get Secure Boot working previously, but I doubt that’s relevant after the upgraded install.

      Based on the info from ipxe.org this is a certificate error. But I’m not sure which certificate that might be or what I could do about it in this case.

      posted in FOG Problems
      T
      thesmj248
    • RE: Issue with active directory

      @bruno67

      Are you sysprepping the image with all OOBE options set to be skipped before capturing it with FOG?

      posted in Windows Problems
      T
      thesmj248
    • Is the client rejecting the custom CA going to cause problems?

      At the behest of my IT Sec department, I installed their custom CA and certs on the FOG server. This makes browsers happy and when connecting to the web interface and more importantly gets their vulnerability scanner to leave me alone.

      However, I’m seeing the following error in the client log:

      ------------------------------------------------------------------------------
      --------------------------------Authentication--------------------------------
      ------------------------------------------------------------------------------
       5/13/2026 3:39:24 AM Client-Info Version: 0.13.0
       5/13/2026 3:39:24 AM Client-Info OS:      Windows
       5/13/2026 3:39:24 AM Middleware::Authentication Waiting for authentication timeout to pass
       5/13/2026 3:41:24 AM Middleware::Communication Download: https://fho-fog/fog/management/other/ssl/srvpublic.crt
       5/13/2026 3:41:24 AM Data::RSA ERROR: Certificate validation failed
       5/13/2026 3:41:24 AM Data::RSA ERROR: Trust chain did not complete to the known authority anchor. Thumbprints did not match.
       5/13/2026 3:41:24 AM Middleware::Authentication ERROR: Could not authenticate
       5/13/2026 3:41:24 AM Middleware::Authentication ERROR: Certificate is not from FOG CA
      
       5/13/2026 3:41:24 AM Client-Info ERROR: Failed to authenticate, will not run Module Looper.
      

      Based on what I can tell from this guide, this is normal behavior as the client is unable to recognize the custom CA without recompiling the client (which I would rather not bother with anyway). What isn’t clear is if this means that the client will continue to work as it should despite not trusting the CA.

      Can I safely ignore this error?
      posted in FOG Problems
      T
      thesmj248
    • RE: Enable SSL/HTTPS without reinstalling FOG?

      Managed to figure it out after looking in the wiki for instructions to uninstall FOG with the intention of reinstalling it. Delete that file, delete the fogproject user, and run the install script again. Now it works.

      posted in General Problems
      T
      thesmj248